Safe Agent Edits
Read rules: folders the agent cannot see
Blocking writes is the obvious half of the policy. Blocking reads is the half people ask for after their first incident.
If an agent can read secrets/, that content ends up in a transcript, in a summary, and in
a context window you do not control. Deleting the file afterwards does not un-send it.
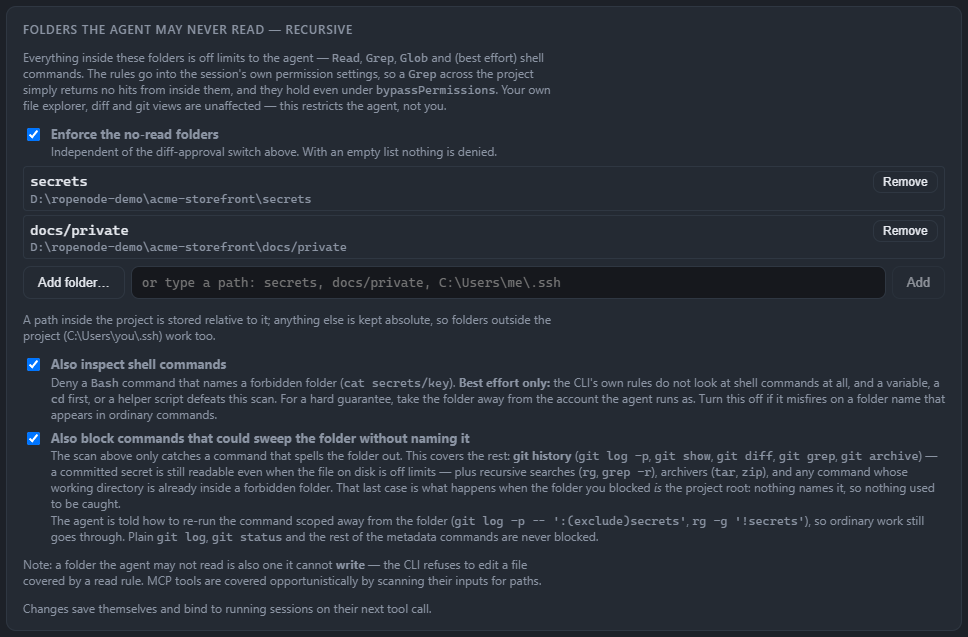
Configure this in Project settings → Safe edits, under Folders the agent may never read.
Nothing is denied by default
Read rules start empty, deliberately. An accidental read-block is far more disruptive than an accidental edit-block: the agent does not fail loudly, it just works from a partial picture and gives you a confidently wrong answer.
Enforced in two places, because one is not enough
- As native permission rules in the session's settings. This is the only layer that can strip denied hits out of Grep and Glob results — otherwise a denied folder still leaks its filenames, and often enough of a matched line to matter.
- In the
PreToolUserelay, which with Also inspect shell commands coversBashtoo, on a best-effort basis.
Commands that read a tree without naming it
This is the case that makes read rules actually work, and it is easy to get wrong.
A no-read folder can be read by anything that sweeps a tree without mentioning the folder at
all: git log -p, git show, git diff, git grep, git archive, recursive greps,
archivers. Scanning the command text for the folder's path never matches any of them.
The worst case: when the denied folder is the project root, the command's working directory is already inside it and the path appears nowhere on the command line.
Also block commands that could sweep the folder without naming it blocks these by command shape rather than by path matching.
Reads outside the project root
Block reads outside the project root too is its own switch, separate from the one for writes, and off by default.
Letting specific outside folders through
A monorepo sibling, a shared vendor directory, a design-token package: add it to Folders outside the project the agent may read and write and it is passed to the CLI as an additional working directory, rather than punching a hole in the whole rule.
Fewer prompts for reads
Don't ask before reading files pre-approves reads and searches everywhere. It runs after every deny, so a no-read folder stays unreadable either way.
Last updated Oct 11, 2026